
Domain DNS Settings
The purpose of this support document is to outline the steps needed to update your domain’s DNS settings. These updates are done to verify your sender domain so that recipient email servers know it is your organization. DonorView is “authorized” to send emails on behalf of your organization once your domain has been verified.
This improves email deliverability but does not guarantee 100% delivery to a recipient’s Inbox. The recipient’s email provider controls the final delivery. Email recipients may have the ability to mark emails as Not Spam, or Trust Sender, or add your organization’s email address to their contacts, which may also improve reaching their Inbox.
There are four (4) records outlined below; the following is a quick outline of the steps needed to update the domain DNS records.
a) If a TXT record exists for the SPF, it is edited. Otherwise, a new TXT for the SPF is added.
b) A new TXT record is added for the DKIM.
c) A new CNAME record is added for the tracking.
d) A new TXT record is added for the DMARC, if one does not exist.
e) Let support know the updates have been made in order to complete the verification.
SPF, DKIM and DMARC FAQs
Setting up your sender domain will help your email reach the inbox.
What is a "Verified Sender Domain"?
A verified sender domain is a domain that has given DonorView permission to send email from your domain. This means that the emails are being sent by DonorView servers, but the emails are using your domain as the "From" address.
Why is it a good idea to verify your sending domain?
Recipient ISPs need to verify that the domain has given permission for DonorView servers to use it. They can verify this by looking up certain records in your domain's DNS.
Where do I start, where do I go to fill in the correct form for this? What will I see?
First, you will go to where your domain is hosted (e.g., GoDaddy, Dreamhost, HostGator etc.), there will be an option there to adjust your DNS settings. You will see several fields of information to fill. The most common are SPF, DKIM.
What are SPF Records?
SPF stands for "Sender Policy Framework". An SPF record is in place to identify which mail servers are authorized to send mail for a given domain. It is used to prevent spammers from sending mail with fraudulent From addresses at that domain.
What are DKIM records?
DKIM stands for "DomainKeys Identified Mail". They allow receiving servers to confirm that mail coming from a domain is authorized by the domain's administrators.
What are DMARC records?
A DMARC policy allows a sender to indicate that their emails are signed by SPF and DKIM, and tells a receiver what to do if neither of those authentication methods passes – such as junk or bounce the email. DMARC removes guesswork from the receiver’s handling of these failed emails, limiting or eliminating the user’s exposure to potentially fraudulent & harmful emails. DMARC also provides a way for the email receiver to report back to the sender about emails that pass and/or fail DMARC evaluation.
DMARC policy on your domain(s) will affect all of your email sending from that domain (not just the mail you are sending through DonorView) so you need to ensure you are using SPF and DKIM for all of your email delivery.
Common Types of DNS Records
- A Record: Maps a domain name to an IPv4 address.
- AAAA Record: Maps a domain name to an IPv6 address.
- CNAME Record: Creates an alias for a domain name, pointing it to another domain.
- MX Record: Specifies the mail servers responsible for receiving email for a domain.
- TXT Record: Stores text-based information, often used for domain verification or email authentication.
- NS Record: Specifies the authoritative name servers for a domain.
- SOA Record: Contains administrative information about the domain.
Instructions for updating the DNS records
1. SPF
a) If the domain DNS has an existing SPF record, then add
“ include:_spf.elasticemail.com ”
to the value with a space before and after the parameter.
For example, your domain DNS already has a TXT record setup for the SPF record and it looks something like:
v=spf1 a mx include:_spf.google.com ~all
The final example record would look like this:
v=spf1 a mx include:_spf.google.com include:_spf.elasticemail.com ~all
b) If the domain DNS does not have an SPF record (please see Note “a” below), then create a TXT record* in your domain DNS settings.
*DNS settings should only have one (1) TXT record for the SPF.
Create a TXT record.
Enter:
Record Type: TXT
Host/Name: enter @ symbol, or use yourdomain.com, or leave blank if the field already points to yourdomain.com.
Value: v=spf1 a mx include:_spf.elasticemail.com ~all
NOTES:
a) If your domain does not have an existing SPF record you may need to “include:” other email service providers (ESP) which you are using. Please check with the ESPs to see if that is required.
b) There is NO SPACE between include: and _spf.elasticemail.com.
2. DKIM
Create a TXT record.
Enter:
Record Type: TXT
Host/Name: api._domainkey
Note: In some systems, select “Other” for the Host/Name and enter the value above as the Other Name.
Value: k=rsa;t=s;p=MIGfMA0GCSqGSIb3DQEBAQUAA4GNADCBiQKBgQCbmGbQMzYeMvxwtNQoXN0waGYaciuKx8mtMh5czguT4EZlJXuCt6V+l56mmt3t68FEX5JJ0q4ijG71BGoFRkl87uJi7LrQt1ZZmZCvrEII0YO4mp8sDLXC8g1aUAoi8TJgxq2MJqCaMyj5kAm3Fdy2tzftPCV/lbdiJqmBnWKjtwIDAQAB
Copy/Paste version below. This is one long text string; NO spaces should be included.
k=rsa;t=s;p=MIGfMA0GCSqGSIb3DQEBAQUAA4GNADCBiQKBgQCbmGbQMzYeMvxwtNQoXN0waGYaciuKx8mtMh5czguT4EZlJXuCt6V+l56mmt3t68FEX5JJ0q4ijG71BGoFRkl87uJi7LrQt1ZZmZCvrEII0YO4mp8sDLXC8g1aUAoi8TJgxq2MJqCaMyj5kAm3Fdy2tzftPCV/lbdiJqmBnWKjtwIDAQAB
Characters for the DKIM Value are shown in Courier New font.
Lowercase L (el) = l
Uppercase I (eye) = I
Numeric 1 (one) = 1
Uppercase O (oh) = O
Numeric 0 (zero) = 0
NOTES:
a) Verify that NO SPACES are included in the Value after it is copied and pasted into the DNS. Place your cursor in the Value field and scroll through it to check for and remove any spaces.
b) DNS settings can have as many DKIM records as needed.
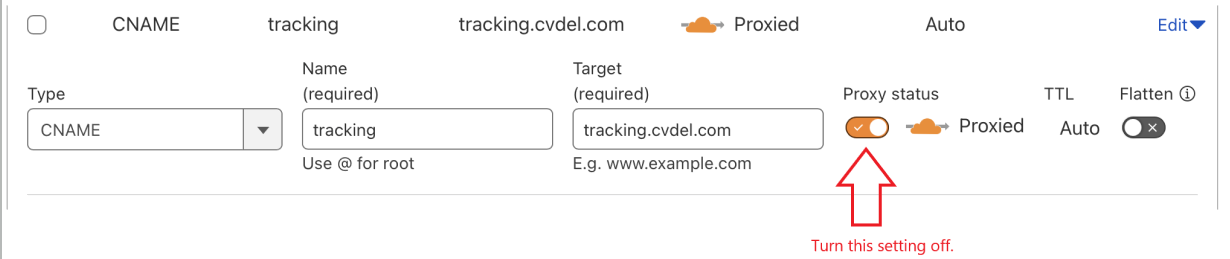
3. Tracking
Create a CNAME record.
Enter:
Record Type: CNAME
Host/Name: tracking
Note: In some systems, select “Other” for the Host/Name and enter the value above as the Other Name.
Value: tracking.cvdel.com
NOTE: If the DNS record has a Proxy setting, turn it off for this record.
4. DMARC
NOTE: Google and Yahoo announced requirements that bulk senders must have DMARC in place beginning February 2024.
Understanding Gmail and Yahoo DMARC Requirements - dmarcian
More information on the DMARC record can be found online (https://dmarcian.com/) to understand its use and impact, but here is an overview:
Report(s) are emailed to the rua= and ruf= mailto addresses entered. The ruf parameter can be skipped.
RUA is reporting that provides an aggregate view of all of a domain’s traffic. The other option is RUF reports that are redacted forensic copies of the individual emails that are not 100% compliant with DMARC. While RUA reports show the traffic of the email, RUF reports contain snippets from the actual emails themselves. While RUA reporting is all that is needed for DMARC deployment, more advanced users may also add the RUF tag, which will send more sensitive information.
Create a TXT record
If the DMARC record has already been setup, this step can be skipped.
The following website can also be used to help generate the record, DMARC Record Wizard.
Enter:
Record Type: TXT
Host/Name: _dmarc
Note: In some systems, select “Other” for the Host/Name and enter the value above as the Other Name.
NOTE:
For the Value,
- replace the youremailaddress@yourdomain.com text in red with a valid email address, if the rua: or rua: and ruf: parameters are included.
Otherwise, remove the rua=mailto:…; and/or ruf=mailto:…; parameter(s) completely.
- For the p= and fo= parameters, only one value should be selected from the choices shown, remove the other p= and fo= parameters, as well as the text in red.
Value: v=DMARC1;p=none; or p=quarantine; or p=reject;(1) pct=100;rua=mailto:youremailaddress@yourdomain.com;ruf=mailto:youremailaddress@yourdomain.com;fo=0; or fo=1; or fo=d; or fo=s;(2)
ADDITIONAL NOTES:
(1) Examples of basic DMARC record Values are shown below; the second record Value listed is suggested, if adding the DMARC:
v=DMARC1;p=none;
v=DMARC1;p=quarantine;
v=DMARC1;p=reject;
If unfamiliar with the DMARC record, the p=none option can be used when setting up the record.
One example is,
v=DMARC1;p= quarantine;pct=100;rua=mailto:youremailaddress@yourdomain.com;
(2) The fo= parameter is optional and is NOT needed if the ruf= parameter is NOT added.
Examples are:
fo=0;
fo=1;
fo=d;
fo=s;
Forensic reporting options. Authorized values: "0", "1", "d", or "s". "0" generates reports if all underlying authentication mechanisms fail to produce a DMARC pass result, "1" generates reports if any mechanisms fail, "d" generates reports if DKIM signature failed to verify, "s" generates reports if SPF failed.
One example is,
v=DMARC1;p= quarantine;pct=100;rua=mailto:youremailaddress@yourdomain.com;fo=0;
5. Validate!
Contact DonorView support so we can validate that the records have been added correctly and complete the verification process.